IT Security Overhaul:
Not a report
and a goodbye.
Every fix, signed off.
A full OWASP Top 10 security audit for CodeIgniter 4, Laravel, WordPress and Shopify platforms. We implement every fix, re-test every finding and deliver a signed security sign-off.
- Report in 48 hours
- Fixes included
- Fixed price before we start
We read your source code, not just run scanners.
Automated tools catch known CVEs. Only manual code review catches IDOR, business logic flaws and developer mistakes.
48hr
Report delivery
0
Outstanding after sign-off
NDA
Before access
What we look for
The vulnerabilities we find on every platform we audit.
Not theoretical risks: real vulnerabilities we found and fixed on real platforms in the last 12 months. At least 4 of these 8 are present on every platform we have audited that was built by multiple developers over time.
Broken access control (IDOR)
Users reach other users' data by changing an ID in the URL. The number one OWASP category in 2024. Found in 5 of the last 6 CI4 platforms we audited.
SQL injection
User input passed straight into database queries without sanitisation, letting attackers dump customer records, payment data and admin credentials.
Broken authentication and sessions
Weak session tokens, no brute-force protection, no lockout after failed logins and sessions that never expire. Account takeover at scale.
Missing CSRF protection
Password changes, payments and admin actions processed without CSRF tokens, so users can be tricked into actions they never meant to take.
Unrestricted file upload
Upload endpoints that accept PHP, executables or oversized payloads. The most dangerous path to remote code execution and full server compromise.
Security misconfiguration
Debug mode in production, default admin credentials, exposed .env files, verbose errors and directory listing. Trivial to exploit and common on shared hosting.
Exposed sensitive data
API keys, database credentials and private keys committed to version control or shipped in client-side JavaScript, especially where many developers have worked.
Vulnerable dependencies
Outdated WordPress plugins, old CI4 versions, unpatched PHP and npm packages with known CVEs. A dependency-level check often reveals 20+ issues in an hour.
Real audit results
What we found and fixed on FliqhtIQ.
Every finding patched, every patch re-tested, and a signed sign-off at the end. These are the ones that mattered most.
- critical IDOR on /student/profile/{id}Any logged-in user could view any student record by changing the ID. No ownership check. Fixed
- high Missing CSRF on admin actionsPassword reset and role change endpoints accepted POST without a CSRF token. Fixed
- critical PHP file upload acceptedProfile photo upload accepted the .php extension. No MIME validation. Fixed
- high Session does not expireAdmin sessions persisted indefinitely with no idle timeout. Fixed
- critical SQL injection in searchThe search parameter was passed unsanitised into a raw query. Fixed
- medium Debug mode in productionThe .env had CI_ENVIRONMENT=development in the production deployment. Fixed
- high Exposed API key in JS bundleA third-party API key was visible in the compiled frontend JavaScript. Fixed
- medium Outdated dependencies5 Composer packages with known CVEs, including one rated 9.8. Fixed
Every finding fixed, re-tested and signed off.
By the numbers
What our audits deliver.
48hr
Report delivery
An audit report with all findings within 48 hours of access being granted.
0
Fixes outstanding
We fix everything and re-test before sign-off. Broken access control is the commonest thing we find, and it is fixed the same way as everything else.
What you get after every audit
- Prioritised findings report (Critical, High, Medium, Low)
- Proof of concept for all critical findings
- All fixes implemented, not just reported
- Re-test confirmation after every fix
- Signed security sign-off document for investor or compliance use
How we audit
Six steps from code access to signed sign-off.
We read source code, not just run scanners. Automated tools catch known CVEs; only manual code review catches IDOR, business logic flaws and developer mistakes.
-
Step 1
Reconnaissance and mapping
We map every route, endpoint, parameter and file upload point in your application. No black-box guessing: we read your source code.
-
Step 2
Automated scan and manual review
Automated tools catch the obvious. Manual review catches the logic flaws, IDOR vulnerabilities and business-logic bypasses that scanners miss.
-
Step 3
Exploitation and proof of concept
For critical findings we produce proof-of-concept exploits: evidence that something is vulnerable, not a note saying it might be.
-
Step 4
Prioritised report delivery
Every finding rated Critical, High, Medium or Low, explained in plain English, with a specific remediation recommendation.
-
Step 5
Fix implementation
We fix every finding ourselves: code patches, configuration changes and dependency updates. All included in the fixed price.
-
Step 6
Re-test and sign-off
Every finding is re-tested to confirm it is resolved, and you receive a signed security sign-off document, useful for investor due diligence.
Audit types
Security audits for every platform we build on.
From a one-off audit of a single application to a monthly retainer for platforms that keep changing.
Fixed price
CI4 and Laravel security audit
A full OWASP Top 10 audit of your CodeIgniter 4 or Laravel application: IDOR, SQL injection, broken auth, CSRF, file uploads, sessions and dependency CVEs, with every fix applied.
Our web development service
Fixed price
WordPress security audit
Plugin vulnerabilities, theme code review, user enumeration, XML-RPC exposure, file permissions and admin hardening. Especially critical for WooCommerce stores handling payments.
Our WordPress development service
Fixed price
Shopify security review
App permission audit, API key exposure check, checkout flow review, metafield injection testing and theme code review for XSS. Applicable to all Shopify Plus stores.
Our Shopify development serviceAuth and session hardening
A Shield auth configuration audit for CI4: session fixation, brute-force protection, remember-me token security, RBAC enforcement and admin lockout policies.
Our web development servicePenetration testing
Manual testing of authenticated and unauthenticated attack surfaces, business logic flaws, API security and privilege escalation paths, delivered with proof-of-concept evidence.
Our web development serviceOngoing security retainer
Monthly monitoring: dependency CVE tracking, log review for anomalous access patterns, quarterly mini-audits and emergency response for security incidents.
Our web development serviceEngagement options
Three ways to engage. All include fixes.
Not just reports. Every option is priced in writing before we start, after we understand the size of your codebase.
One-time Security Audit
Full OWASP audit + all fixes implemented + re-test + sign-off. Fixed price, agreed before we start. Duration: 1 to 2 weeks depending on codebase size.
Get a fixed priceAudit + Hardening Sprint
Audit first, then a focused 2-week hardening sprint - auth system review, dependency updates, server configuration hardening, and admin access controls.
Get a fixed priceOngoing Security Retainer
Monthly: dependency CVE monitoring, quarterly mini-audits, log anomaly review, and emergency incident response. For platforms with continuous development.
Get a fixed priceNDA before any access is granted.
Everything is confidential. Tell us your platform and roughly how many routes it has, and we will come back with a fixed price and a timeline.
Security work
Platforms we have audited and hardened.
Ground Zero
Laravel platform for a talent search and advisory firm serving India's social impact sector, combining a job board, an events and podcast archive and a blog behind one CMS.
Read the case study4 Live
Content Modules
Full CMS
Admin Editability
None to Full CMS
Active
Community Groups
None to Growing
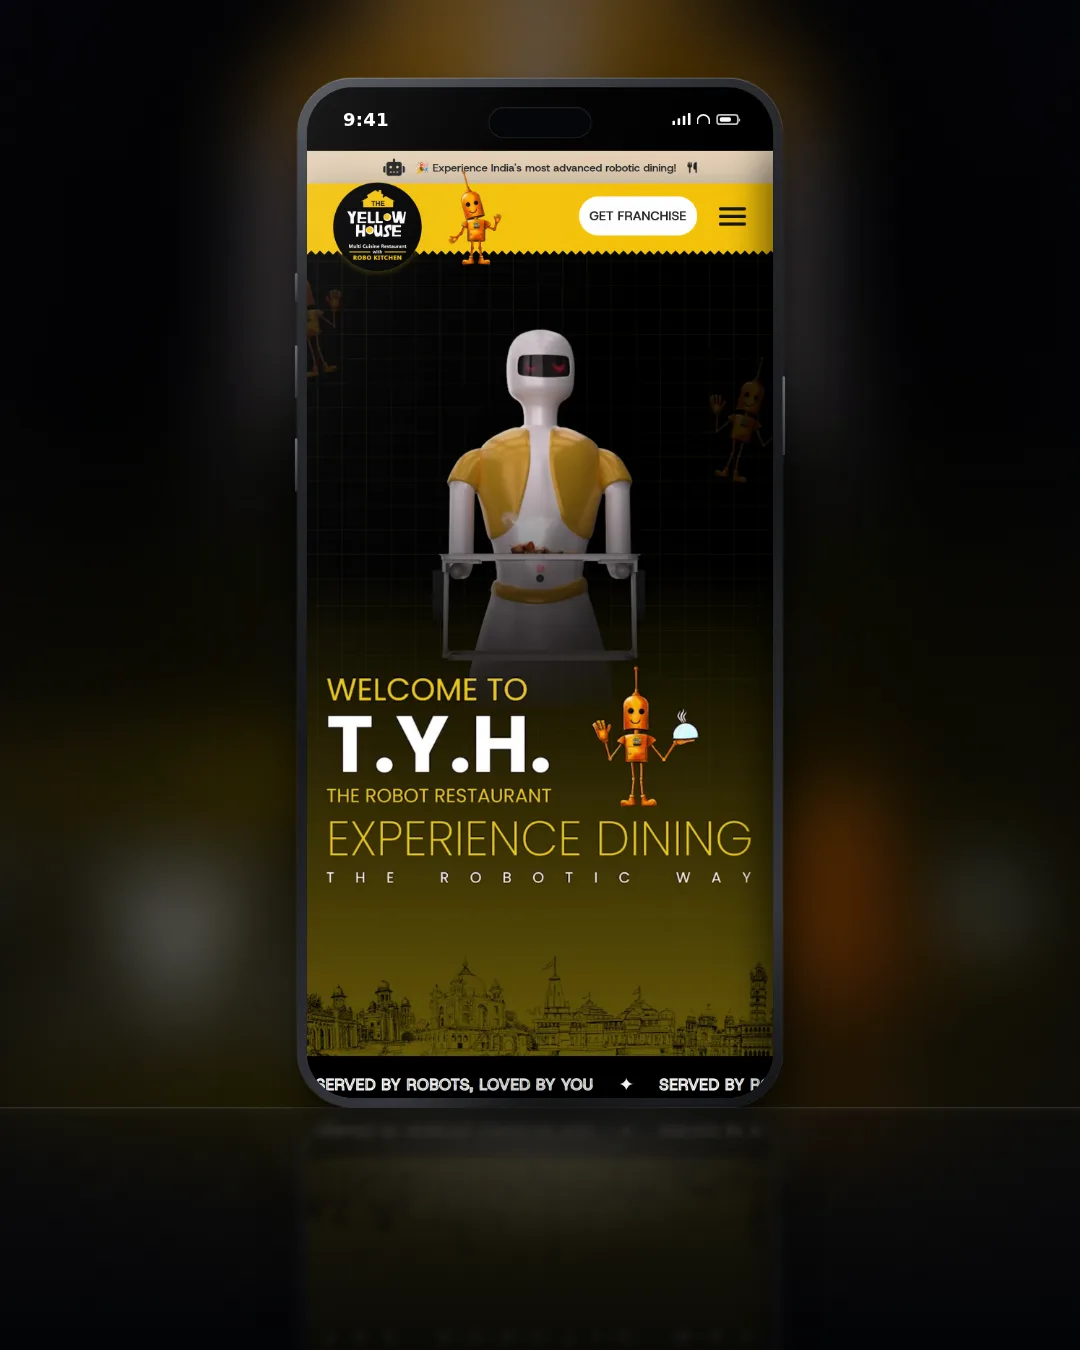
Food & Hospitality · Hospitality
Robot Restaurant India
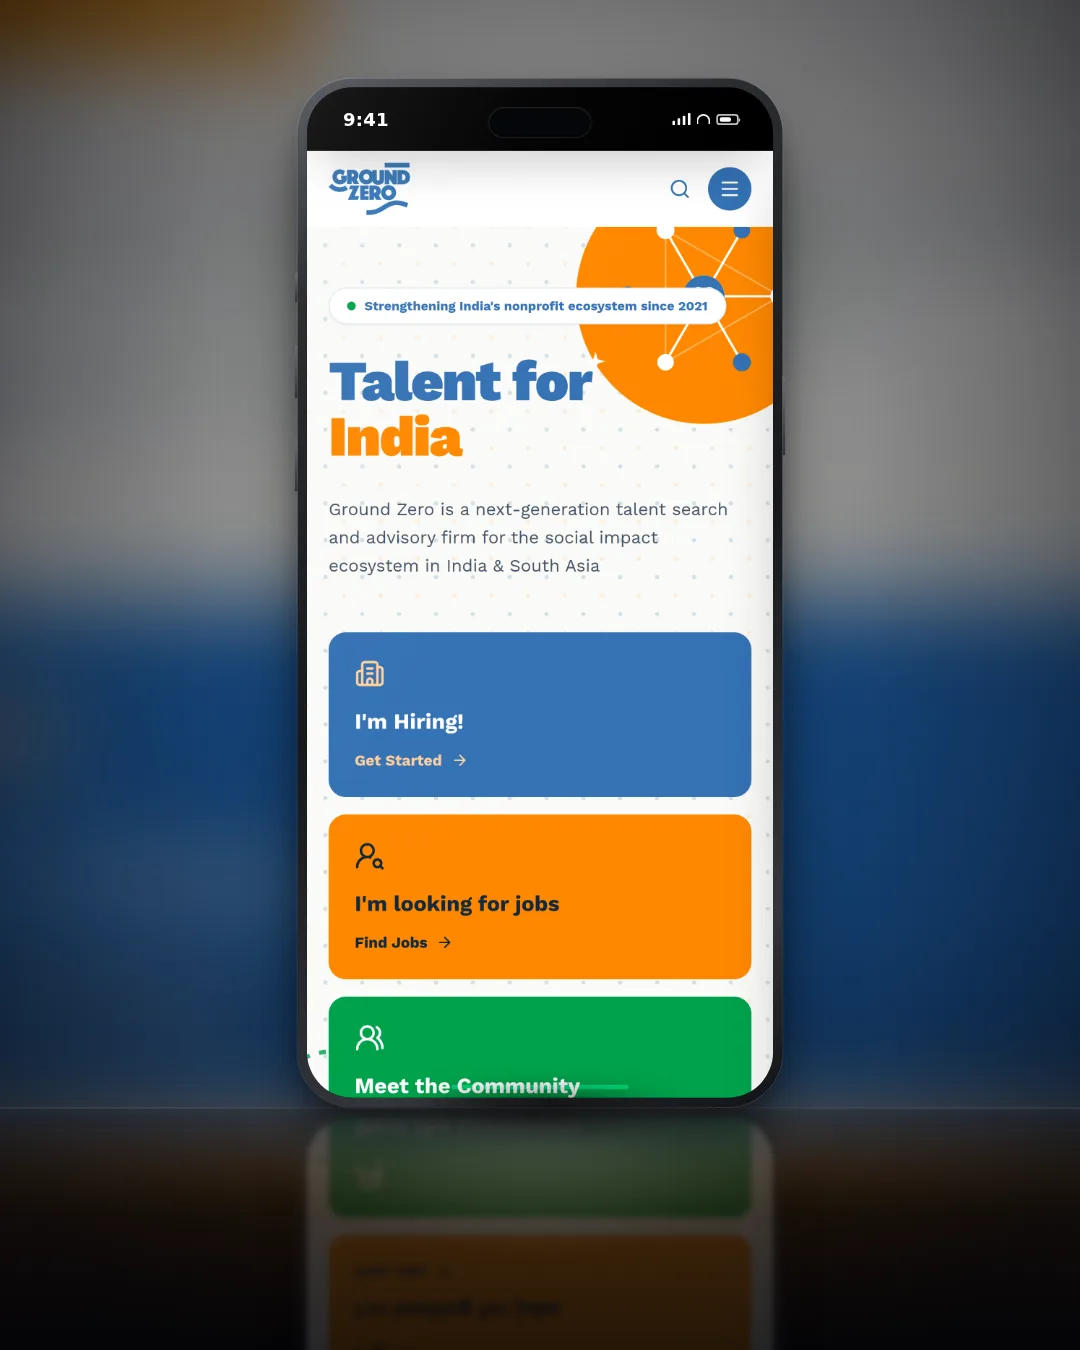
Talent Search & HR Advisory · Recruitment
Ground Zero
4 Live content modules
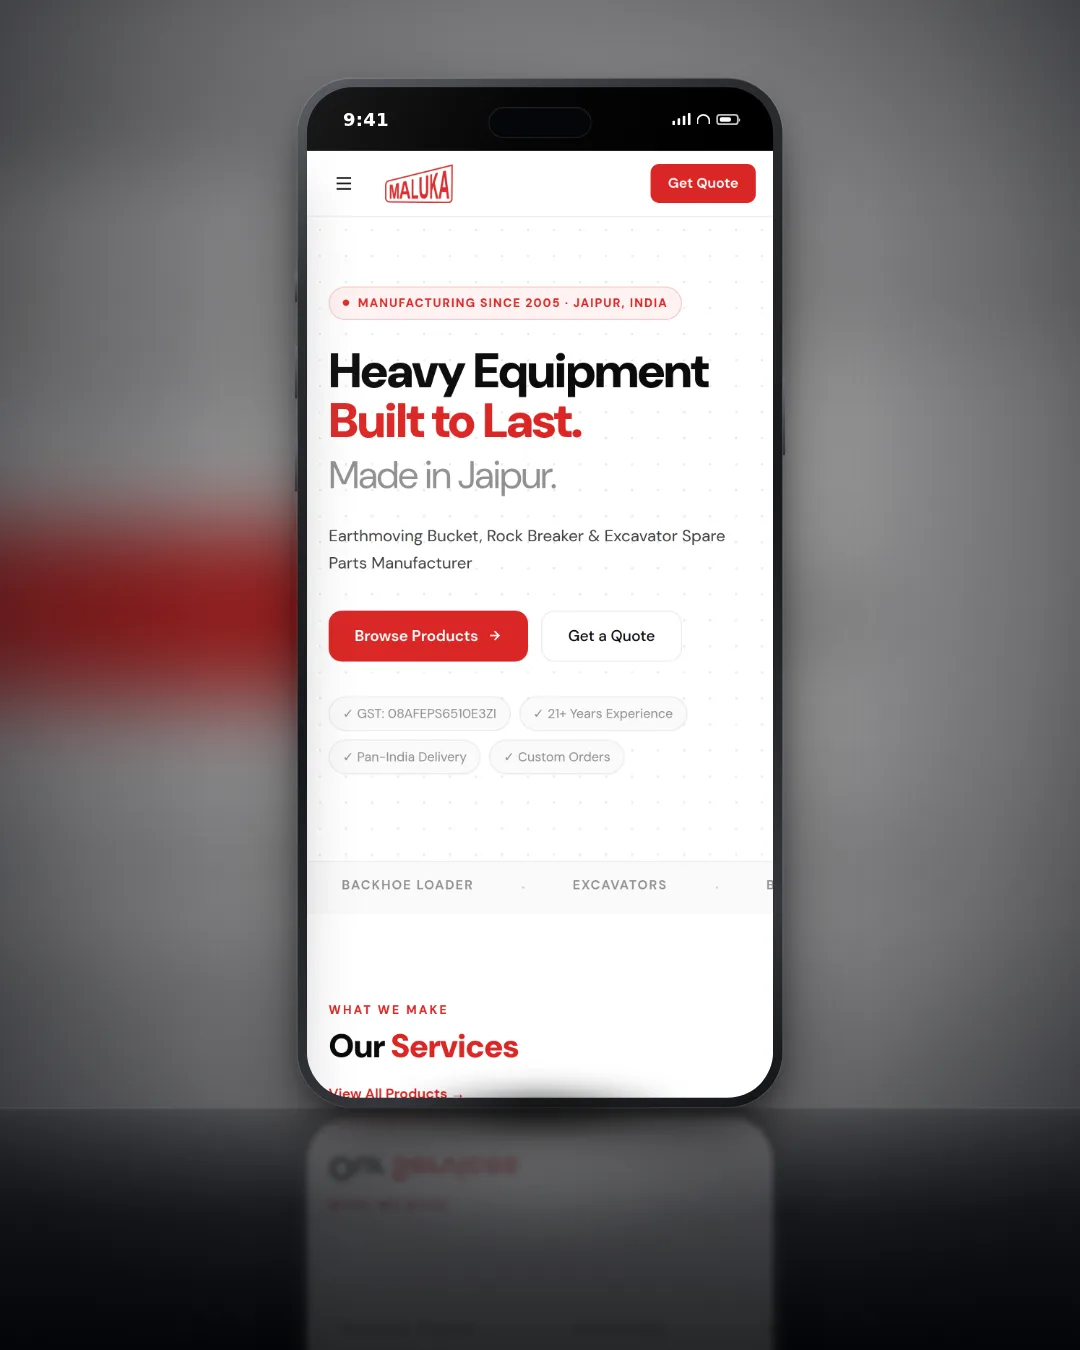
Heavy Equipment / Construction · CodeIgniter 4
Maluka Earthmovers
Hardened auth system
See every case study
Shopify, WordPress and custom builds, with the brief, the work and the result.
View all workFAQ
Security questions we answer every week.
NDA signed before any access is granted. Everything is confidential.
CodeIgniter 4, Laravel, WordPress including WooCommerce, and Shopify. We read your source code rather than only running an automated scanner. That is why our audits find logic flaws and IDOR vulnerabilities that automated tools miss entirely, alongside the known CVEs and misconfigurations a scanner does pick up.
We fix everything. Every finding in the report is patched by us: code changes, configuration updates and dependency upgrades. You receive a re-test confirmation and a signed sign-off document. We do not hand over a 40-page PDF and leave, and the fixes are included in the fixed price agreed before we start.
One to two weeks for a standard web application with under 50 routes. Larger platforms with complex role systems take two to three weeks. We agree the timeline before starting and deliver on it, and the findings report itself arrives within 48 hours of access being granted, so fixing can start early.
A structured report: an executive summary, the full findings list with severity ratings, a technical description of each vulnerability, proof-of-concept evidence for critical issues and remediation notes. Alongside the report you get the implemented fixes and a re-test confirmation, ending in a signed security sign-off.
Yes. We sign an NDA before receiving any access or code. All findings, client names and vulnerability details are confidential, and we do not reference a client's security findings without explicit written permission. Confidentiality covers the whole engagement, from first access to final sign-off.
Yes, and it is one of the most common reasons clients come to us. Investors increasingly ask for security sign-off on a platform before a Series A. We deliver a signed re-test document confirming that all critical and high findings have been resolved, which you can share during due diligence.
The OWASP Top 10 categories as they show up in real PHP and eCommerce platforms: broken access control and IDOR, SQL injection, broken authentication and sessions, missing CSRF protection, unrestricted file upload, security misconfiguration, exposed secrets and vulnerable dependencies. Manual review also covers business logic specific to your application.
Within 48 hours of access being granted. The report ranks every finding by severity, with proof of concept for the critical ones, so the most dangerous issues are fixed first. We then implement the fixes, re-test each one and close with a signed sign-off and zero fixes outstanding.
Yes, through the ongoing security retainer: monthly dependency CVE monitoring, quarterly mini-audits, log review for anomalous access patterns and emergency incident response. It suits platforms with continuous development, where new code and new dependencies keep changing the attack surface after the first audit.
Reading that goes with this.
Local SEO for a Jaipur Business: Google Business Profile, Citations and the Map Pack
The map pack is ranked on three things Google names publicly, and only two of them are yours to change. Here is what that means in practice for a Jaipur business, and which of the usual local SEO advice is a waste of your time.
Moving From WooCommerce to Shopify: A Migration Checklist That Protects Your Rankings
Most of the risk in a WooCommerce to Shopify move is not the product data. It is the URL map, the things that were plugins and now have to be rebuilt, and in India the payment gateway, which does not come across at all.
eCommerce SEO for Shopify Stores in India: The Work That Actually Ranks Product Pages
Shopify handles a lot of technical SEO for you and leaves a specific set of problems it cannot fix. Here is which pages to fight for, the duplicate URL trap every store has, and what to do about supplier product copy.
IT security overhaul
Your platform has vulnerabilities. Find them before someone else does.
NDA before access. Fixed price before we start. Every finding patched before sign-off.
NDA first
Signed before we see any code or access.
Report in 48 hours
Every finding ranked by severity.
Fixed and signed off
Every fix re-tested, zero outstanding.
Book a security audit
Tell us your platform (CI4, Laravel, WordPress or Shopify), roughly how many routes it has and why you want an audit now.